

- Administer the Covata Platform (through Safe Share Administration and/or Safe Share Organization Administration), as well as to
- Create encrypted files (i.e. Secure Objects (1) ) within an organization,
- Access and decrypt an encrypted file’s/Secure Object’s data and
- Utilize Covata Safe Share applications.
- Has permission to administer organizations that utilize the Covata Platform and its associated Covata technologies.
- Is represented by a user account which can be added, edited (by the user themselves) as well as removed (as well as re-added again) by any other Safe Share administrator through the Administrators page.
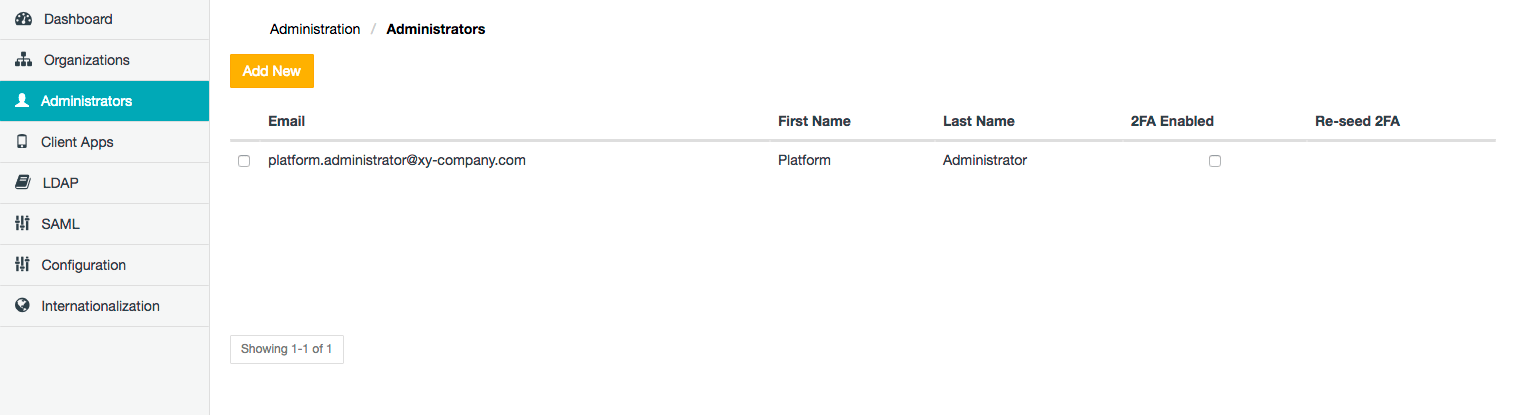
A Safe Share administrator user’s fields
Each Covata user’s account is defined by a set of fields described in the table below, of which only the Email field can be specified when a Safe Share administrator’s account is added account through Safe Share Administration. A Safe Share administrator user can configure their own user account’s fields when they edit their own account. Unless stated in the following table, these fields and their values are visible on the Administrators page of Safe Share Administration.
(2) While a Safe Share administrator can modify these fields’ values for their Covata user account via the My Account feature through Safe Share Administration, the user can also modify these values via equivalent features in the Safe Share web application and other Safe Share products, as well as Organization Administration (assuming they are a member of at least one organization and have the required roles to access these features). A Safe Share administrator becomes a member of an organization when:
- they create a new organization through Safe Share Administration and make themselves the administrator of this organization, or
- an existing Organization administrator of that organization adds this Safe Share administrator’s user account to their organization.
Other fields are associated with a Safe Share administrator’s user account. However, these fields are either:
- only visible through the ‘Users’ page of Safe Share Organization Administration, or
- used internally by the Covata Platform and are therefore only exposed to a limited extent through user interfaces (or not exposed at all).
Safe Share administrators and user roles
Each Covata user must be assigned a role, which grants the user access to different sets of features available through the Covata Platform and Covata technologies. A Covata user is automatically granted the Safe Share administrator role when their user account is added through Safe Share Administration.Users can have more than one role (as explained in more detail in the following table):
- A user with the Safe Share administrator role can also be granted the Organization administrator role for any organization.
- A user with either of these administrator roles can also be granted either the Originator or Collaborator role for any organization.
- Likewise, a user with either the Originator or Collaborator role in any organization can have the Safe Share administrator and/or Organization administrator roles.
Adding a Safe Share administrator account
This procedure describes how to add a Safe Share administrator user account to the Covata Platform. This process grants the Covata user the Safe Share administrator role. To add a Safe Share administrator user to the Covata Platform:- Sign in to Safe Share Administration.
- Click the Administrators option on the left of the Safe Share Administration interface to open the Administrators page.
- Click the Add New button.
- In the Add New Safe Share Administrator dialog box, specify the email address of the user.
-
Click Save and the user (now a Safe Share administrator) will appear as a new entry on the Administrators page.
Notes:-
If this user’s email address has not yet been registered on the Covata Platform, a new Covata user account is automatically created for them. This user’s:
- Covata user account will have the Local account type, which is only visible through the ‘Users’ page of Safe Share Organization Administration and
- email address is sent an ‘account created’ email notification, with instructions on how to sign in (to Safe Share Administration). The initial sign-in process usually requires the Safe Share administrator to reset their password immediately after signing in.
- If this user already has a user account on the Covata Platform, their account is granted the Safe Share administrator role (and if this user account was not already a member of any organization, their account is enabled). Although this user is not sent an email notification as a result of being granted the Safe Share administrator role, this user will be able to access Safe Share Administration the next time they sign in.
-
If this user’s email address has not yet been registered on the Covata Platform, a new Covata user account is automatically created for them. This user’s:
Removing Safe Share administrators
Removing a Covata user account from Safe Share Administration:- removes the Safe Share administrator role from the user account and
- prevents the user from gaining access (through this account) to the Safe Share Administration interface and its features.
Removing a Covata user account from Safe Share Administration does not delete this account from the Covata Platform. If a Covata user (previously removed from Safe Share Administration) is added back again or granted other user roles (which would provide the user with access to features such as Secure Object handling and manipulation within their organization/s on the Covata Platform), then the same user account is re-utilized. Any fields that the user had previously edited/customized are retained.
- Sign in to Safe Share Administration.
- Click the Administrators option on the left of the Safe Share Administration interface to open the Administrators page.
- Find the Safe Share administrator whose account is to be removed from Safe Share Administration and select their check box on the left.
-
Click the

The selected user accounts are removed from Safe Share Administration and will no longer have access to the Safe Share Administration interface and its features.
Editing your Safe Share administrator account
This procedure describes how to edit the fields of your (Safe Share administrator) user account on the Covata Platform. To edit your Safe Share administrator user account:- Sign in to Safe Share Administration.
- Click your email address at the top-right of the page and choose My Account from the drop-down menu.
-
In the Account Details section of the subsequent page, update any of your user account’s fields (described in detail above).
Note: The Email addresses of all Covata user accounts on the Covata Platform are unique and since this field may be used for auditing purposes, no Covata user account’s email address field can be edited. However, to update the email address of your user account and/or those of other Safe Share administrators, then for each of these users:- Add a new Safe Share administrator account (with their new email address). For each account whose Account Type is LDAP, obtain the new email address from your LDAP server/user directory administrator in order to add their account (with this email address) to Safe Share Administration.
- Remove the user’s old Covata user account.
-
Click Save and your user account’s fields will be updated.
Notes:- If you cannot edit your user account’s fields, then your Account Type is likely to be LDAP. (Be aware that additional field information, such as the Account Type, are only visible through the ‘Users’ page of Safe Share Organization Administration.) The fields of LDAP user accounts are edited through their respective LDAP servers’ user directories and are updated on the Covata Platform during synchronization events with these user directories. See Configuring LDAP for more information.
- Other than your own Covata user account, it is not possible to edit the fields (above) of any other Covata user accounts.
Changing your Safe Share administrator account password
Only a Covata user with the Local Account Type who has signed in to either the Safe Share web application or Safe Share Administration can change their own password.The authentication of an LDAP user on the Covata Platform is delegated to its respective LDAP server. If you have an LDAP user account and wish to change its password, you will need to contact your LDAP administrator for details on how to do this (e.g. through the user account on your LDAP server/user directory). See Configuring LDAP for more information.
- Sign in to Safe Share Administration.
- Click your email address at the top-right of the page and choose My Account from the drop-down menu.
- In the Security section of the subsequent page, click the Change password button.
- On the Set your password… page, specify your current password and then your new password twice (i.e. once more to verify it).
- Click the Change button and your Covata user account’s password is now changed.
Terminating your Safe Share administrator account’s sessions
Terminating your Safe Share administrator account’s sessions immediately invalidates all of your currently valid access/refresh tokens. This will sign you out of every Safe Share application with which you have an active session, including any client applications that use the Covata Platform’s resources. This feature is useful if your Safe Share administrator account is at risk of being compromised - for example, you suspect that you forgot to sign out from a shared computer or you were signed in from a laptop that was either lost or stolen before you signed out. To terminate your Safe Share administrator account’s sessions:- Sign in to Safe Share Administration.
- Click your email address at the top-right of the page and choose My Account from the drop-down menu.
- In the Security section of the subsequent page, click the Terminate button.
All of your active sessions with the Covata Platform are terminated immediately, which also results in you being signed out from your current session. You will need to sign in again to gain access to Safe Share and/or your Covata Platform’s resources.
Enabling or disabling 2FA for a Safe Share administrator
If required, any Safe Share administrator user account (including your own) can be configured with two-factor authentication (2FA) by enabling this feature on their account. If 2FA has been enabled on a user account, then in order to successfully sign in through this account on the Covata Sign-in page, the user will be required to enter both their password (i.e. the 1st authentication factor) as well as an authentication code obtained from an authenticator application (aka authenticator app) running on the user’s mobile device (i.e. the 2nd authentication factor). The 2FA feature supports the following mobile devices and authenticator apps:- Android-based devices running the Google Authenticator app,
- Apple’s iPhone, iPad or iPod Touch devices running the Google Authenticator app, or
- Microsft Windows-based devices running Microsoft’s authenticator app.
- Before enabling 2FA on a Safe Share administrator account, you may wish to confirm if the user of this account is in possession of any one of these supported mobile devices (above), or notify the user that they will require access to one of these devices to continue signing in through the Covata Sign-in page.
- The URLs to download the appropriate authenticator app for a supported device are available to users when they configure 2FA on their accounts (and are themselves configurable through the Configuration page).
- Sign in to Safe Share Administration.
- Click the Administrators option on the left of the Safe Share Administration interface to open the Administrators page.
- Find the Safe Share administrator (or Safe Share administrators) account/s whose 2FA settings are to be enabled or disabled.
-
Do either of the following:
-
To enable 2FA on the account/s, select the check box/es (in the 2FA Enabled column) of the relevant user account/s, which immediately enables 2FA on the account/s.
Each Safe Share administrator with 2FA enabled in this manner is sent an email notification informing them that 2FA has been enabled for their account. This email message contains a time-limited link, which leads to step-by-step instructions for the user to:- Configure their mobile device with the appropriate authenticator app.
- Configure the authenticator app (once installed) with their Covata user account, so that the authenticator app can generate the appropriate authentication codes (for the 2nd authentication factor).
-
To disable 2FA on the account/s, clear the check box/es (in the 2FA Enabled column) of the relevant user account/s, which disables 2FA on the account/s.
Each Safe Share administrator with 2FA disabled in this manner is sent an email notification informing them that 2FA has been disabled for their account.
-
To enable 2FA on the account/s, select the check box/es (in the 2FA Enabled column) of the relevant user account/s, which immediately enables 2FA on the account/s.
Re-configuring 2FA for a Safe Share administrator
While two-factor authentication (2FA) is enabled on a Safe Share administrator’s account, the user might lose the ability to generate authentication codes for their 2nd authentication factor (explained in more detail above) due to any of the following reasons:- The Safe Share administrator deleted their Covata user account configuration from the authenticator application (app) installed on their mobile device.
- The time-limited link for configuring 2FA expired before the Safe Share administrator had a chance to complete the 2FA configuration process. This is the link contained in the email notification informing the Safe Share administrator that 2FA has been enabled on their account.
- The Safe Share administrator lost their mobile device. The user will require a replacement device in order to continue signing in through the Covata Sign-in page with 2FA enabled on their account.
- Sign in to Safe Share Administration.
- Click the Administrators option on the left of the Safe Share Administration interface to open the Administrators page.
- Find the Safe Share administrator (or Safe Share administrators) whose user account/s are to be re-configured for 2FA.
-
Click the Re-seed button (in the Re-seed 2FA column) associated with the account/s. This button is only available on Safe Share administrator accounts with 2FA already enabled.
Each Safe Share administrator with 2FA re-configured in this manner is sent an email notification informing them that 2FA has been enabled for their account, similar to the email notification they received when 2FA was enabled on their account. This email message contains a new time-limited link, leading to step-by-step instructions for the user to:- (Re-)configure their mobile device with the appropriate authenticator app (should the user need to conduct this step again).
- (Re-)configure the authenticator app (once installed) with their Covata user account, which allows the authenticator app to generate the appropriate authentication codes for the 2nd authentication factor.