

- Create encrypted files (i.e. Secure Objects (1) )
- Access and decrypt an encrypted file’s/Secure Object’s data
- Utilize Covata Safe Share applications
- Administer the Covata Platform (through Covata Administration).
- Has permission to access these features based on their roles.
- Is represented by an account which can be added, edited as well as disabled or re-enabled by a Covata Platform administrator through the Users page.
Note: Users may also be added and updated through an LDAP connection. However, only the roles and valid access/refresh tokens (i.e. sessions) of an LDAP user can be managed through Covata Administration.
-
Covata-encrypted data that has been registered on the Covata Platform.
Note: Covata-encrypted data is data from a file or stream, which has then been encrypted either:- Using Covata technologies (i.e. with a Covata Safe Share product or another client application that utilizes the Covata Platform’s API for encryption via the Content Service), or
- According to Covata’s encryption requirements (i.e. a client application with its own encryption implementation). For more information about Covata’s encryption requirements, see the Required parameters on POST section on the
<content-service>/api/v1/objects/{objectId}/contentspage of the Covata API documentation .
- The metadata associated with this encrypted data. Some of this metadata can be determined by the creator/owner of the Secure Object.
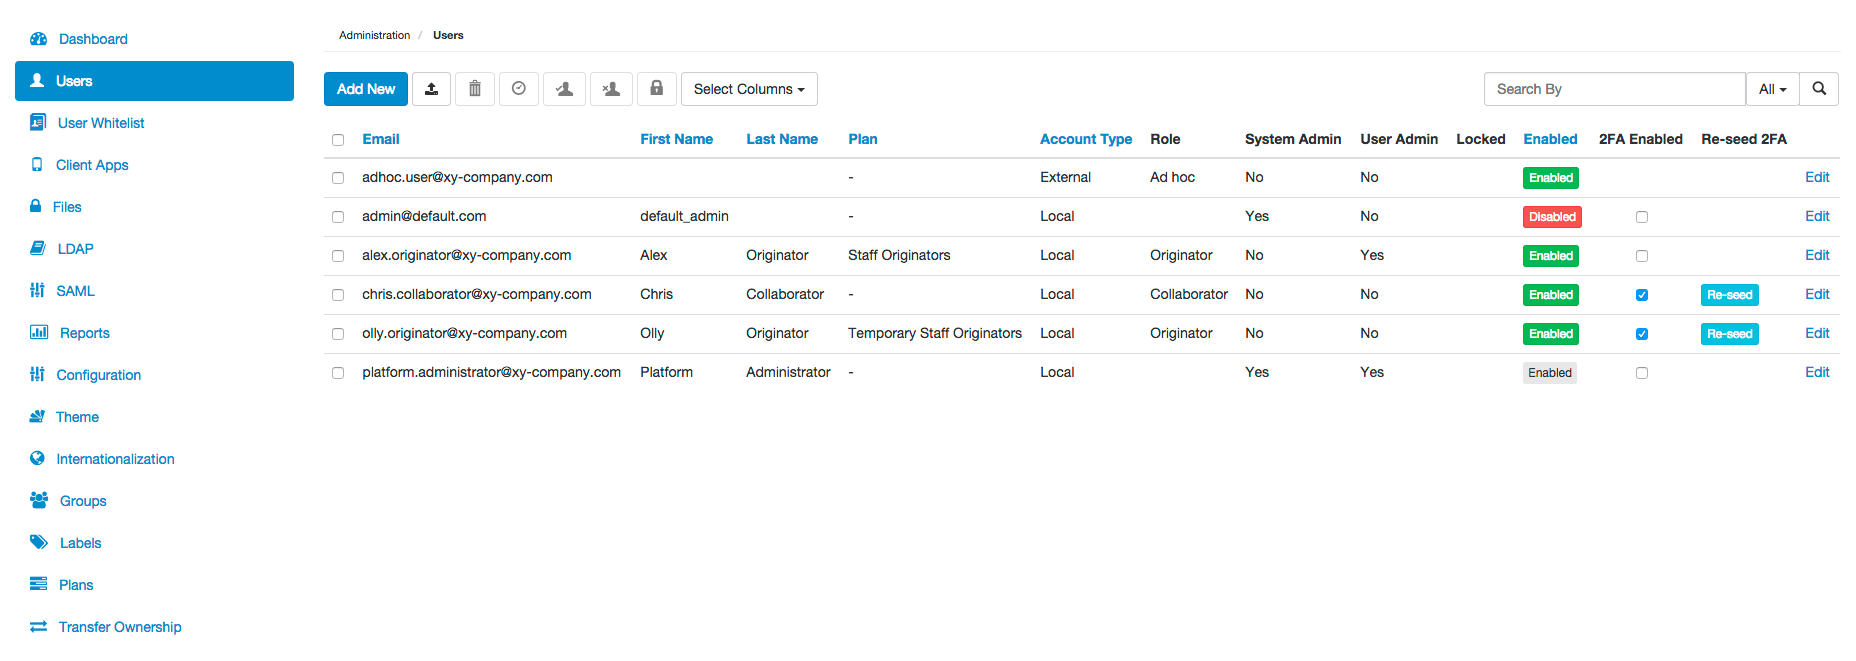
A user’s fields
Each Covata user’s account is defined by a set of fields (of which only a subset are required to add a valid user). A Covata Platform administrator is able to configure these fields when:- Adding any new Local user to the Covata Platform or
- Editing a Local or External user.
(2) These values may be modified by a Covata user themselves when they update their account details through the My Account feature of the Covata Safe Share web application.
A user’s roles
Each Covata user must be assigned a role, which grants the user access to different sets of features available through Covata technologies. A Covata user’s roles can be modified by editing their user account.Some users can have more than one role:
- A user with the System administrator and/or User administrator roles can also be granted either the Originator or Collaborator role.
- Likewise, a user with either the Originator or Collaborator role can also be granted the System and/or User administrator roles.
Adding a new user
This procedure describes how to add a Local user account to the Covata Platform.- Local user accounts can also be added in bulk (in a single action) from a CSV file.
- To add users from an LDAP server/user directory, see Configuring LDAP.
- Sign in to Covata Administration.
- Click the Users option on the left of the Covata Administration interface to open the Users page.
- Click the Add New button.
- In the Add User dialog box, complete the user’s fields (described in detail above).
Tip: See A user’s roles for more information about the role(s) to specify for this user. - By default, the Covata Platform requires the new user to reset their password upon signing in for the first time; to do this, the new user requires the Covata Platform’s automatically generated password which is emailed to them after their account has been created. To prevent the Covata Platform from forcing this password reset, clear the Force Password Reset check box.
- Click Save and the new user will appear as a new entry on the Users page.
Note: The new user is sent an email notification, with instructions on how to sign in to the Safe Share web application.
Adding new users in bulk (from CSV)
New Local users can be added in bulk (in a single action) by importing their details from a CSV file. CSV file preparation and requirements- The Covata Platform’s CSV user import feature assumes that each line of the CSV file (except the first mandatory ‘header’ line) contains field data for a specific user. (The first line will not be imported as a user.)
-
The order of field data for each user in the CSV file (as should be defined by the header line) must be:
Email, First Name, Last Name, Mobile number, Role, Force Password Reset flag
Notes:- White space around each separating comma is not required.
- You can specify any field names/labels for the header line of your CSV file. However, the order of field data for each user (in subsequent lines of your CSV file) must comply with the order above.
-
For a user to be successfully imported from a CSV file, the following conditions must be met:
- The data values for the
EmailandRolefields are mandatory. All other field values are optional. - The
Rolefield value can only be exactlyOriginatororCollaborator(i.e. an initial capital letter followed by lower-case letters). It is not possible to import Covata users with the Ad hoc, System administrator or User administrator roles. - The values for
EmailandMobile numbermust be valid and comply with the relevant field’s requirements. - To specify no data for an optional field, specify nothing followed by a comma to indicate the next field - for example, to only specify the
EmailandRolefields for the Covata userfred.bloggs@xy-company.comwho has the Originator role, your CSV line for this user would be:
fred.bloggs@xy-company.com,,,,Originator, - A valid value for the
Force Password Reset flagfield is an ALL CAPITALS, lower case or Title Case boolean value - i.e.TRUE,True,true,FALSE, etc. If no value is specified, a value offalseis assumed.
- The data values for the
- Sign in to Covata Administration.
- Click the Users option on the left of the Covata Administration interface to open the Users page.
-
Click the

- In the Import from CSV dialog box, click the Choose a file button.
-
Navigate to and select your CSV file containing the users to be imported to the Covata Platform.
The CSV import feature proceeds to import your users. Upon completion, the number of successfully imported Covata users are reported, along with each unique invalid data value (if any were encountered). - Click Close to close the Import from CSV dialog box.
- The number of users that can be imported from a single CSV file is restricted by the response timeout of the Covata Platform’s load balancer. We found that a response timeout of 60 seconds on our load balancers allowed the import of up to 1000 users from a CSV file. If you have your own on-site deployment of the Covata Platform, you may wish to tweak the response timeout of your load balancers to allow the import of more users from a CSV file.
- When a new Local user account is created, the Covata Platform automatically generates a password which is emailed to that user. To maximize security, the password (once created), is hashed 64,000 times using the PBKDF2 algorithm before being stored by the Covata Platform. Since this process has an overhead of approximately 300 milliseconds and the number of users imported by the CSV user import feature could be extensive, then the auto-generated passwords of CSV-imported Covata users are only hashed 100 times using PBKDF2 (before being stored by the Covata Platform). Hence, if you are concerned about the security of these stored passwords, you may wish to ensure that the
Force Password Reset flagvalue for each user’s line of your CSV file isTRUE.
Finding existing users
As more users are added to the Covata Platform, it can become difficult to locate specific users through the Users page of Covata Administration. The Users page therefore offers features to help you locate specific user accounts more rapidly. To locate specific user accounts on the Covata Platform:- Sign in to Covata Administration.
- Click the Users option on the left of the Covata Administration interface to open the Users page.
-
Use either of the following features to find a specific user account (or subset of these accounts):
- Filter user accounts - In the Search by… box (right of the Users page), begin typing a series of characters contained in any of the users’ Email, First Name, Last Name, Role or (System) Admin fields. This filters the list of users on the Covata Platform to those whose Email, First Name, Last Name, Role or (System) Admin (i.e. ‘yes’ or ‘no’) contains the subset of characters entered into the Search by… box.
By default, the Email, First Name, Last Name, Role or (System) Admin fields are used for filtering (i.e. All), although filtering can be restricted to just one of these fields using the adjacent drop-down. - Navigate to specific user accounts - Use the page navigation buttons (lower-right of the Users page), which work in conjunction with the adjacent 25/50/75/100 items (i.e. user accounts) per page dropdown.
- Filter user accounts - In the Search by… box (right of the Users page), begin typing a series of characters contained in any of the users’ Email, First Name, Last Name, Role or (System) Admin fields. This filters the list of users on the Covata Platform to those whose Email, First Name, Last Name, Role or (System) Admin (i.e. ‘yes’ or ‘no’) contains the subset of characters entered into the Search by… box.
Editing an existing user
This procedure describes how to edit the fields of an existing Local or External (i.e. Ad hoc) user account on the Covata Platform. It is also used for modifying the roles of an LDAP user account.The other fields of LDAP user accounts can only be edited through their respective LDAP servers’ user directories. These user accounts get updated on the Covata Platform during synchronization events with the LDAP server. See Configuring LDAP for more information.
- Sign in to Covata Administration.
- Click the Users option on the left of the Covata Administration interface to open the Users page.
- Locate the Local or External/Ad hoc user account whose fields are to be edited.
- Click the Edit link of the relevant user (towards the right of the page).
-
In the Edit User dialog box, update the relevant user’s fields (described in detail above).
Notes:- The Email address of all users on the Covata Platform is unique and since this field is used for auditing purposes, it cannot be edited. To update the email address of a Local user, add a new account for them and either disable or delete their old user account.
- For more information about the Force Password Reset check box, see Forcing users to reset their passwords.
- Click Save and the user’s fields will be updated.
Changing your password
Only a Local user who has signed in to either Safe Share web application or Covata Administration can change their own password.The authentication of an LDAP user on the Covata Platform is delegated to its resepctive LDAP server. If you have an LDAP user account and wish to change its password, you will need to contact your LDAP administrator for details on how to do this (e.g. through the user account on your LDAP server/user directory). See Configuring LDAP for more information.
- Sign in to Covata Administration.
- Click your email address at the top-right of the the Covata Administration interface and choose Change Password from the drop-down menu.
- On the Set your password page, specify password and then your new password twice (once to confirm it).
- Click the Change button and your Covata user account’s password is now changed.
Deleting users
Deleting Covata user accounts removes these users from the Covata Platform, including:- All of the encrypted files/Secure Objects and folders/collections which these users currently own.
- All reporting data associated with these users’ accounts.
- The Covata Platform’s log files still retain a record of activities conducted by Covata users whose accounts have been deleted.
- To disable Covata users, which prevents them from accessing Covata technologies through their user accounts (but retains all aspects of these users’ encrypted files, folders and reporting data), see Disabling or re-enabling users.
- The user account with which they are currently signed in to Covata Administration.
- LDAP user accounts (see Notes below).
- Sign in to Covata Administration.
- Click the Users option on the left of the Covata Administration interface to open the Users page.
- Find the user/s whose accounts are to be deleted.
- Select their check box/es on the left (or select the top check box in the user list’s header to select all check boxes of the currently visible user accounts).
-
Click the

The selected user accounts are removed, along with the encrypted files, folders and reporting data that belonged to these user accounts.
If an LDAP user account is deleted (using this procedure above), the account itself is deleted temporarily until the Covata Platform next synchronizes with the LDAP server, upon which the account reappears amongst the list of Covata users. However, the LDAP user’s encrypted files, folders and reporting data are still removed. Hence, to permanently ‘delete’ an LDAP user account from the Covata Platform:
- Disable the LDAP user through the account’s LDAP server/user directory.
- Delete the LDAP user account through Covata Administration (using this procedure above).
- ( Optional ) Delete the LDAP user through the account’s LDAP server/user directory. If you do not delete the account through the LDAP server/user directory, the user account will reappear amongst the list of Covata users when the Covata Platform next synchronizes with the LDAP server. However, the account will be disabled.
Expiring users’ tokens/sessions
Expiring users’ access/refresh tokens forces all of these users’ currently signed in sessions to terminate immediately. The users will then be required to sign in again to gain access to Safe Share and/or their Covata Platform’s resources. This feature is useful when one or more Covata user accounts are at risk of being compromised - for example, these Covata users either forgot to sign out from a computer used by more than one person, or they were signed in on their laptop, which was either lost or stolen before they signed out. To expire users’ access/refresh tokens:- Sign in to Covata Administration.
- Click the Users option on the left of the Covata Administration interface to open the Users page.
- Find the user/s whose accounts are to have all their access/refresh tokens expired.
- Select their check box/es on the left (or select the top check box in the user list’s header to select all check boxes of the currently visible user accounts).
-
Click the

All access/refresh tokens associated with the selected user accounts are expired immediately.
Disabling or re-enabling users
Disabling Covata user accounts prevents access to the Covata Platform through these accounts. This is useful when, for example, one or more people leave an organization and are no longer permitted to be an Originator or access Covata technologies through their organization’s user accounts. However, it may be necessary to retain:- All of the encrypted files/Secure Objects and folders/collections which have been created through these people’s user accounts.
- All reporting data associated with their accounts.
- The Covata user accounts themselves, in the event that one or more of these people rejoin the organization at a later point in time (when their original accounts can be re-enabled).
- The user account with which they are currently signed in to Covata Administration.
- LDAP user accounts (see Note below).
- Sign in to Covata Administration.
- Click the Users option on the left of the Covata Administration interface to open the Users page.
- Find the user/s whose accounts are to be disabled, enabled or re-enabled.
-
For a single user account, to:
- Disable it - click the account’s green Enabled button (in the Enabled column) until the button changes red and indicates Disabled.
- Enable or re-enable it - click the account’s red Disabled button (in the Enabled column) until the button changes green and indicates Enabled.
- Select their check boxes on the left (or select the top check box in the user list’s header to select all check boxes of the currently visible user accounts).
-
Then, to:
-
Disable these accounts - click the

The users’ accounts are disabled and their green Enabled buttons (in the Enabled column) change to red Disabled ones. -
Enable or re-enable these accounts - click the

The users’ accounts are enabled/re-enabled and their red Disabled buttons (in the Enabled column) change to green Enabled ones.
- If any selected user accounts were already disabled or enabled upon clicking the above Disable Users or Enable Users buttons, respectively, then this action is ignored on these accounts.
- It is not possible to both disable and enable/re-enable different sets of user accounts in a single action.
-
Disable these accounts - click the
LDAP user accounts cannot be disabled or re-enabled through Covata Administration, because the state of these user accounts is controlled through their LDAP server/user directory. For example, if an LDAP user has been disabled through its LDAP user directory, this account will appear Disabled on the Users page and it will not be possible to enable or re-enable the account through this page.
Forcing users to reset their passwords
Local users can be forced to reset their password (for example, because you have increased the password complexity or suspect that one or more users’ passwords may have been compromised). To force Local users to reset their passwords:- Sign in to Covata Administration.
- Click the Users option on the left of the Covata Administration interface to open the Users page.
- Find the user/s whose passwords need to be changed.
-
For a single user account:
- Click the Edit link of the relevant user (towards the right of the Users page).
- In the Edit User dialog box, select the Force Password Reset check box and click Save.
- Select their check boxes on the left (or select the top check box in the user list’s header to select all check boxes of the currently visible user accounts).
-
Click the

All of these user accounts’ passwords will be reset.
- The value of the Force Password Reset check box is effectively ignored if you are editing a user account with the Ad hoc role, since these types of users can only authenticate through a one-time access link/password.
- LDAP users can only reset their password through their account’s LDAP server/user directory.
Unlocking users’ accounts
If a Covata user enters their password incorrectly more than the Covata Platform’s configured maximum, then the user’s account becomes locked. The user is also sent an email notification with instructions on how to unlock their account and allow it to be used again. On the Users page, locked Covata user accounts have a red Unlock button (in the Locked column), which Covata Platform administrators can use to manually unlock any other user’s account.A Covata Platform administrator can only unlock Covata user accounts which have been locked as a result of breaching the configured maximum of ‘Email my password’ attempts.
- Sign in to Covata Administration.
- Click the Users option on the left of the Covata Administration interface to open the Users page.
- Find the user/s whose account is to be unlocked.
- Click the red Unlock button (in the Locked column) of the relevant user/s, which immediately unlocks their user account/s.
Enabling 2FA on a user account
If required, any Covata user account can be configured with two-factor authentication (2FA) by enabling this feature on their account. If 2FA has been enabled on a user account, the user is then required to enter both their password (i.e. the 1st authentication factor), as well as an authentication code obtained from an authenticator application (aka authenticator app) running on their mobile device (i.e. the 2nd authentication factor), in order for the user to successfully sign in through this account on the Covata Sign-in page. The 2FA feature supports the following mobile devices and authenticator apps:- Android-based devices running the Google Authenticator app,
- Apple’s iPhone, iPad or iPod Touch devices running the Google Authenticator app, or
- Microsft Windows-based devices running Microsoft’s authenticator app.
- Before enabling 2FA on a Covata user account, you may wish to confirm if the user of this account is in possession of any one of these supported mobile devices (above), or notify the user that they will require access to one of these devices to continue signing in through the Covata Sign-in page.
- URLs to download the appropriate authenticator app for a supported device are available (and configurable) through the Themes page.
- Sign in to Covata Administration.
- Click the Users option on the left of the Covata Administration interface to open the Users page.
- Find the user/s whose account is to be configured with 2FA.
-
Select the check box (in the 2FA Enabled column) of the relevant user/s, which immediately enables 2FA for these user account/s.
Each user with 2FA enabled in this manner is sent an email notification informing them that 2FA has been enabled for their account. This email message contains a time-limited link, which leads to step-by-step instructions for the user to:- Configure their mobile device with the appropriate authenticator app.
- Configure the authenticator app (once installed) with their Covata user account, so that the authenticator app can generate the appropriate authentication codes (for the 2nd authentication factor).
Re-configuring 2FA for a user account
While two-factor authentication (2FA) is enabled on a user’s account, the user might lose the ability to generate authentication codes for their 2nd authentication factor (explained in more detail above) due to any of the following reasons:- The user deleted their Covata user account configuration from the authenticator application (app) installed on their mobile device.
- The time-limited link for configuring 2FA expired before the user had a chance to complete the 2FA configuration process. This is the link contained in the email notification informing the user that 2FA has been enabled on their account.
- The user lost their mobile device. The user will require a replacement device in order to continue signing in through the Covata Sign-in page with 2FA enabled on their account.
- Sign in to Covata Administration.
- Click the Users option on the left of the Covata Administration interface to open the Users page.
- Find the user/s whose account is to be re-configured for 2FA.
-
Click the Re-seed button (in the Re-seed 2FA column) of the relevant user/s to re-configure 2FA for their account.
Each user with 2FA re-configured in this manner is sent an email notification informing them that 2FA has been enabled for their account, similar to the email notification they received when 2FA was originally enabled on their account. This email message contains a new time-limited link, leading to step-by-step instructions for the user to:- (Re-)configure their mobile device with the appropriate authenticator app (should the user need to conduct this step again).
- (Re-)configure the authenticator app (once installed) with their Covata user account, which allows the authenticator app to generate the appropriate authentication codes for the 2nd authentication factor.
Configuring columns on the ‘Users’ page
By default, all columns on the Users page are visible. With the exception of the Email column (which is always shown), if there are other columns whose visibility is not required when administering users on your Covata Platform instance, then these columns can be selectively hidden from the Users page. To hide one or more columns from the ‘Users’ page, or make these columns visible again:- Sign in to Covata Administration.
- Click the Users option on the left of the Covata Administration interface to open the Users page.
- Click the Select Columns drop-down and clear the check boxes next to the column names to be hidden. Conversely, select the check boxes next to the column names to be made visible again.